OpenAI is preparing another round of internal security testing and has enlisted some unexpected allies. It is partnering with the mysterious startup Cathedral, founded by a group of former young associates of Elon Musk from the government agency DOGE. The company only recently came to public attention when, according to its own account, it breached the internal systems of rival company Anthropic.
According to OpenAI, Cathedral researchers will use its artificial intelligence models and work alongside its teams to test where the company has weaknesses. OpenAI’s reasoning is simple. Artificial intelligence is getting better at finding security vulnerabilities, and those defending systems must deploy it before attackers do.
Breaching Anthropic in Less Than a Day, or in Several Days?
Cathedral gained notoriety for accessing Anthropic’s private systems through a program in which the company pays for discovered vulnerabilities. Representatives of the startup told the Washington Post that it took them less than twelve hours. They also listed what they had accessed, including Slack messages, job offers, and meeting transcripts.
Anthropic, however, disputes their version of events. Cybersecurity chief Logan Graham wrote on X that the breach actually took several days. According to him, the attackers did not reach the company’s most sensitive areas, namely model weights and users’ conversations with Claude. Graham also noted that Cathedral’s approach was unusual and fell outside the rules Anthropic had established for finding vulnerabilities. The hackers had built their attack around several vulnerabilities in third-party software.
As AI becomes more capable at finding vulnerabilities, defenders need to put it to work before attackers do. We’re planning our next internal security sprint at OpenAI and partnering with Cathedral Systems, whose researchers will use our models alongside our teams to challenge our defenses. They’ll bring differentiated expertise and approaches to our ongoing work to find and fix weaknesses with AI. We’re also raising bug bounty rewards, including more than quadrupling rewards for critical findings. Exceptional findings will be eligible for up to $172,000, including bonuses. We’ll keep advancing our models, using them to strengthen our own systems, and expanding access for trusted defenders. https://t.co/vcaoHROTt2
— OpenAI (@OpenAI) November 3, 2026
Higher Rewards and Alarm Over PHP
The partnership with Cathedral is only one part of the plan. OpenAI also announced that it is increasing rewards for people who find security vulnerabilities in its systems. It will pay more than four times the previous amount for the most serious findings, while exceptional discoveries could earn up to $172,000 including bonuses. The company did not specify the baseline from which it is calculating the increase. Gizmodo notes that OpenAI announced last March that it was raising its maximum reward from $20,000 to $100,000, but it is not yet clear whether the new increase is based on that amount. On X, OpenAI promised to continue improving its models, use them to protect its own systems, and give vetted security professionals access to them.
The company is responding to an event that put the cybersecurity industry on high alert, much like the fear surrounding the Y2K problem once did. In late October, researchers uncovered serious vulnerabilities in PHP, a decades-old programming language that powers roughly 70 percent of websites. Governments and other organizations around the world took their websites offline as a precaution to prevent attacks and hurriedly deploy a fix.
An OpenAI model helped find the PHP vulnerabilities. The company then launched a global initiative called Patch the Planet, aimed at finding and fixing other vulnerabilities that may be hidden in widely used software. In a blog post, OpenAI wrote that recent incidents in the industry show how quickly new threats can emerge and why weaknesses must be continuously identified and fixed before someone exploits them.
The Young Men from DOGE and Their Mysterious Company
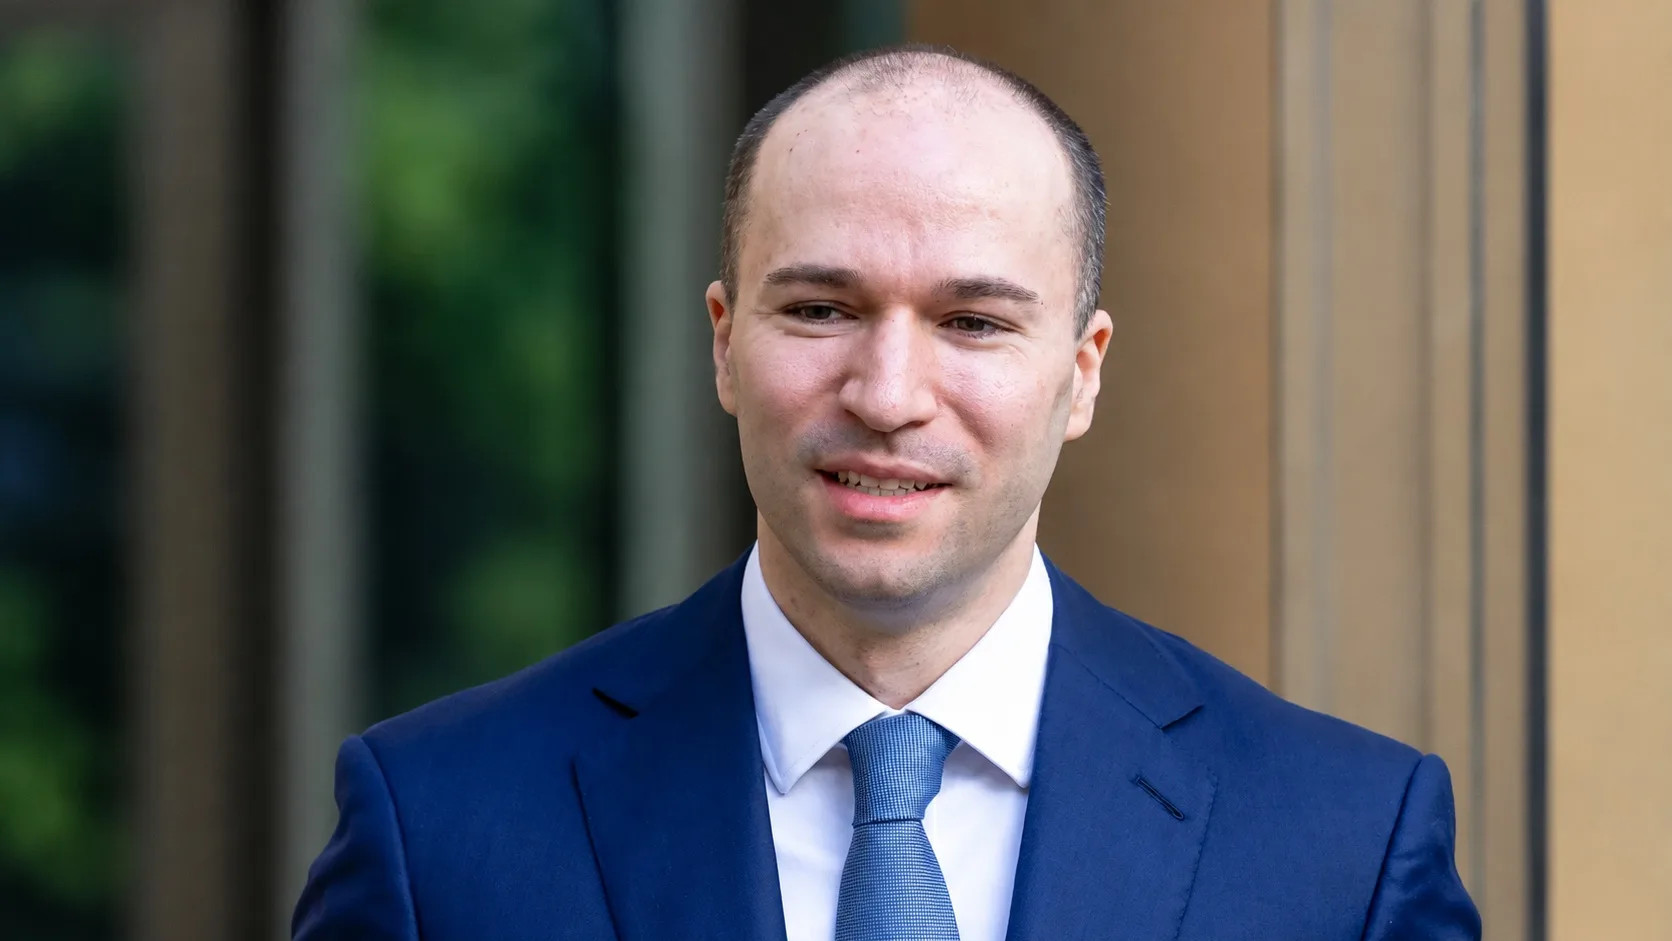
Startup founders Gavin Kliger, Luke Farritor, Marko Elez, and Jack Stein were among Elon Musk’s young aides at the short-lived DOGE agency. At the beginning of Donald Trump’s second term, it was tasked with cutting federal spending and pushed more than a quarter of a million government employees out of their jobs.
Kliger, who leads Cathedral as its chief executive, previously worked as a developer at Databricks. According to his LinkedIn profile, he served as chief data officer at the U.S. Department of War from December through April of this year. Farritor completed an internship at SpaceX and received a Thiel Fellowship in 2024. He was also part of a team that won $700,000 in the Vesuvius Challenge after using artificial intelligence to decipher an ancient papyrus scroll charred in a volcanic eruption.
Elez worked at SpaceX, X, and xAI. He became known for leaving DOGE after the Wall Street Journal linked him to an anonymous X account filled with racist posts. After Vice President JD Vance defended him, Musk quickly promised to take him back, adding that to err is human and to forgive divine. Journalists were unable to determine the exact identity of the fourth founder, Jack Stein.
Cathedral was founded this year, and after a $160 million funding round led by Andreessen Horowitz and Sequoia Capital, investors valued it at $1.4 billion. In July, Reuters cited unnamed sources as saying that the company wants to strengthen the U.S. military’s offensive and defensive cyber capabilities against adversaries such as China. In public, however, the startup reveals very little about itself. Its website consists only of the company’s name in white lettering against a black background, while its X profile has no posts or logo, only a terse description about protecting critical American infrastructure.
Source: gizmodo.com